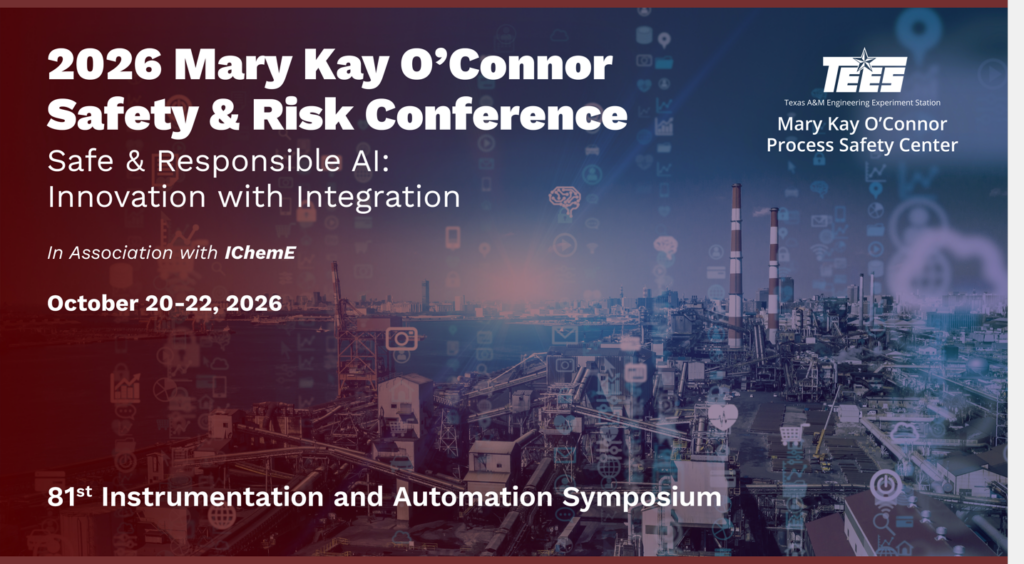
Armexa is pleased to announce that John Cusimano, our Chief Strategy Officer, will speak at the 2026 Mary Kay O’Connor Safety & Risk Conference, hosted by the Mary Kay O’Connor Process Safety Center at Texas A&M. The conference runs October 20 through 22 at the Sonesta Hotel Houston IAH Airport. This year’s theme is “Safe & Responsible AI: Innovation with Integration.”
Session Details
- Title: If Your Control System Isn’t Secure, It Isn’t Safe
- Date: Tuesday, October 20, 2026
- Time: 5:00 to 5:30 PM CT
- Location: Sonesta Hotel Houston IAH Airport, Houston, TX
- Agenda: View the full conference agenda (PDF)
About the Talk
Plants may look the way they did decades ago, but the technology inside them has changed a great deal. Ethernet, Windows, virtualization, cloud connectivity and now AI have all reached control and safety systems. The programmable, connected layers are the basic process control system, the alarm system and the safety instrumented system (SIS), and in many plants they carry most of the risk reduction credited in LOPA.
John’s central point is that a cyber attack is both an initiating event and a potential common-cause failure of those protection layers, so it belongs in the process safety risk analysis. LOPA multiplies the failure probabilities of independent layers to reach a figure such as 10⁻⁴ per demand. If the BPCS and SIS share a network, an engineering workstation, credentials or a platform, one compromise can defeat all of them at once while the worksheet still shows the same number.
John will cover:
- Why deliberate, repeatable cyber attacks do not fit the failure-rate models used for SIL and PFD calculations.
- What TRITON, the first known malware built to attack a safety instrumented system, taught the industry.
- What IEC 61511 already requires: since the 2016 edition, clause 8.2.4 calls for a security risk assessment of the SIS and clause 11.2.12 for SIS designs that are resilient to the identified risks.
- How ISA/IEC 62443-3-2, ISA TR84.00.09 and IEC TR 63069 connect cybersecurity to the safety lifecycle.
- How Cyber HAZOP and Cyber Bowtie reuse existing PHA and LOPA data to produce a risk-ranked mitigation plan, illustrated with a tank overfill scenario.
Attendees will leave with a more practical way to describe cyber risk in operational terms that safety teams and leadership both understand, and a clearer view of common-cause paths between control and safety systems that often go unnoticed.
About John Cusimano
John has spent nearly 40 years working across reliability, security and safety in industrial systems. He is an ISA Fellow and holds the CISSP, GICSP and CFSE credentials. He chairs ISA/IEC 62443-3-2 and is a voting member of ISA99/IEC 62443 and API 1164. He is also a member of ISA84/IEC 61511 and serves on the ISASecure Technical Steering Committee. John helped pioneer the CyberHAZOP and CyberBowtie methods.
Connect With Us
If you’re attending, plan to join John’s session on October 20. Learn more and register at mkosymposium.org. To set up a meeting with John or the Armexa team during the conference, contact us at armexa.com.